KVM vs OpenVZ: Which VPS Virtualization Wins?
Key takeaways
- KVM gives each VPS its own kernel and hardware-assisted isolation, so your resources are dedicated rather than shared with neighbors.
- OpenVZ runs containers that share the host kernel, which lowers overhead but blocks custom kernels and can lead to oversold RAM.
- For workloads that need reliable performance, custom kernel modules, or Windows, KVM is the safer choice.
- You can confirm what your host runs in seconds with systemd-detect-virt or by checking for /proc/user_beancounters.
KVM vs OpenVZ compared: full virtualization with a dedicated kernel versus shared-kernel containers, plus how to check what your host runs.
For most real workloads, KVM wins. It gives each VPS its own kernel and hardware-assisted isolation, so the CPU, RAM, and disk you pay for are actually yours. OpenVZ is lighter and can be cheaper, but it shares one kernel across every container on the machine, which limits what you can run and opens the door to noisy neighbors. This guide explains the difference in plain terms, walks through the performance and security trade-offs, and shows you how to check what your own host is running.
If you are comparing VPS plans and keep seeing "KVM" and "OpenVZ" in the specs, the choice matters more than the marketing suggests. It changes whether you can run Docker cleanly, load a custom kernel module, or trust that your advertised 4 GB of RAM is really there when you need it.
TL;DR
- KVM is full virtualization. Each VPS boots its own kernel and gets hardware-level isolation through Intel VT-x or AMD-V. Resources are dedicated.
- OpenVZ is container-based virtualization. Every container shares the host's single kernel. Overhead is low, but isolation and flexibility are weaker.
- Pick KVM when you need guaranteed resources, custom kernels, Docker, Windows, or predictable performance.
- Pick OpenVZ only when the price is very low and your workload is a simple, single-purpose Linux app that never touches the kernel.
How KVM full virtualization differs from container-based OpenVZ
The two technologies solve the same problem, splitting one physical server into many, but they do it at completely different layers.
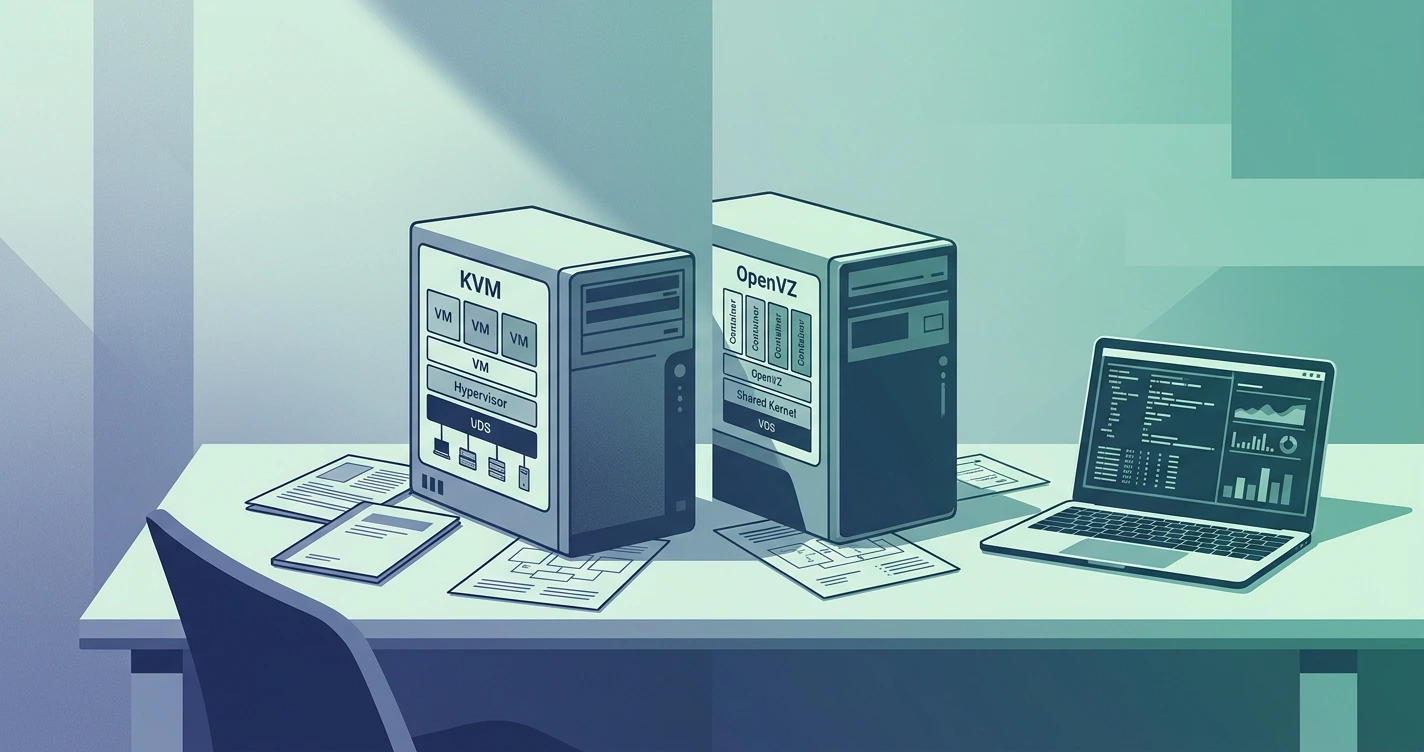
KVM (Kernel-based Virtual Machine) turns the Linux kernel itself into a hypervisor. Each virtual machine runs as a native Linux process, scheduled and managed by the kernel like any other program, and boots a full guest operating system with its own kernel. Because it relies on hardware virtualization extensions (Intel VT-x, AMD-V), the guest thinks it is running on real hardware. According to Red Hat's documentation, KVM was announced in 2006 and merged into the Linux kernel a year later, and it now supports a wide range of guest architectures.
OpenVZ takes the container approach. Instead of emulating hardware, it partitions a single running kernel into isolated user spaces. As the OpenVZ project documentation describes, each container gets its own root access, users, IP addresses, processes, files, and libraries, but they all share the host's kernel. There is no second operating system booting inside the container. That is why OpenVZ has less overhead, and also why it is more restrictive.
A simple way to picture it: KVM gives every tenant their own house with their own plumbing. OpenVZ gives every tenant a locked apartment in one building that shares the same water main.
| Aspect | KVM | OpenVZ |
|---|---|---|
| Virtualization type | Full (hardware-assisted) | OS-level containers |
| Kernel | Dedicated per VM | Shared host kernel |
| Custom kernel / modules | Yes | No |
| Guest OS options | Any Linux, BSD, Windows | Host-compatible Linux only |
| Resource isolation | Strong (hardware-level) | Namespace-level |
| Overhead | Slightly higher | Very low |
| Risk of oversold RAM | Low | Higher (burst / vSwap models) |
Resource isolation, dedicated RAM, and custom kernels explained
This is where the abstract difference becomes a practical one.
Dedicated versus shared resources
On a KVM host, the RAM assigned to your VPS is allocated to your VM. When a plan says 4 GB, the hypervisor reserves that memory for your guest. A busy neighbor cannot silently eat into it.
OpenVZ can behave differently. It historically supports memory models such as burst RAM and vSwap, which let a provider advertise a generous limit while betting that not every container hits its ceiling at once. That works fine until the host gets crowded, at which point your "guaranteed" memory can vanish under contention. Not every OpenVZ provider oversells, but the model makes it possible in a way KVM does not.
Custom kernels and modules
Because a KVM guest boots its own kernel, you can:
- Load custom kernel modules
- Run a different OS family entirely, including Windows or BSD
- Use WireGuard, custom iptables/nftables modules, or tuned network stacks
- Run nested virtualization and clean Docker or Kubernetes setups
None of that is available on OpenVZ. Containers must run on the host's kernel, so you are stuck with whatever kernel version and modules the provider chose. If your application needs /dev/tun, a specific kernel feature, or a non-Linux OS, OpenVZ simply cannot do it.
Root access with a catch
Both give you root, but OpenVZ root is limited. You administer your environment, yet you cannot touch anything that lives at the kernel level, because that kernel belongs to the host and every other container on the box. KVM root is the real thing, all the way down to the bootloader.
Performance and security trade-offs for real workloads
Neither technology is universally faster. They win in different places.
Raw density and micro-overhead. OpenVZ has an edge in pure overhead. With no second kernel to boot and no hardware emulation layer, containers start fast and pack tightly onto a host. For a provider selling very cheap, single-purpose Linux boxes, that density is the whole point.
Consistent performance under load. KVM wins here. Hardware-assisted isolation means one tenant's CPU spike or disk thrashing is far less likely to bleed into your VM. On modern hardware the virtualization overhead is small, and what you lose in theoretical density you gain in predictability. For a database, a game server, or an API that has to stay responsive, predictable beats marginally faster.
Security isolation. This is the clearest gap. A KVM guest is separated from the host by the CPU's virtualization extensions, so a compromise inside one VM has a much smaller blast radius. OpenVZ containers share one kernel, which means a single kernel vulnerability can potentially affect every container on the machine, and the host along with them. For anything handling untrusted input or sensitive data, that shared-kernel surface is a real consideration.
For the practical workloads people actually run, the pattern is consistent:
- Game servers (Minecraft, Rust): KVM. They need reliable CPU and RAM, and often custom Java or networking tuning. Our VPS game server hosting buyer's guide goes deeper on sizing these.
- Docker and Kubernetes: KVM. Containers-inside-containers work cleanly on a dedicated kernel.
- Windows workloads: KVM only. OpenVZ cannot boot Windows at all.
- A single small Linux daemon on a tight budget: OpenVZ can be acceptable, if you accept the limits.
Why ByteHosty runs pure KVM VPS
ByteHosty runs every VPS on KVM, full stop. The reasoning follows directly from the trade-offs above: dedicated resources and hardware-level isolation are what let us promise a spec and mean it.
That choice shapes the rest of the platform. Each ByteHosty VPS gets a dedicated kernel, so you can load modules, run Docker, deploy Windows Server with RDP, or reinstall a different OS whenever you want, all with genuine root access. Because memory and CPU are allocated to your VM rather than pooled and oversold, a busy neighbor does not degrade your box. Plans run on Intel Xeon hardware with NVMe SSD storage and DDR4 ECC memory, include unmetered traffic and AS203446 SmartMitigate DDoS protection, and are managed through the Virtualizor control panel. If you are moving from a shared-kernel container to a real VM, our step-by-step guide to setting up a VPS server walks through the first boot.
The short version: KVM is the foundation that makes the rest of the specs trustworthy.
How to tell what virtualization a host actually uses
Some providers are vague about virtualization, and a few sell OpenVZ while implying more. You do not have to take their word for it. Once you have SSH access, a few commands settle it in seconds.
1. Use systemd-detect-virt (the fastest check).
On any modern systemd Linux system, run:
systemd-detect-virt
Per the systemd-detect-virt manual page, it prints kvm for a KVM virtual machine and openvz for an OpenVZ container. If it prints none, you are on bare metal. The command exits 0 when it detects virtualization and non-zero otherwise, so it is easy to script.
2. Check for the OpenVZ fingerprint.
OpenVZ containers expose a file that KVM machines do not have:
cat /proc/user_beancounters
If that file exists and prints a table of resource limits, you are on OpenVZ. If you get "No such file or directory," you are almost certainly not.
3. Cross-check with virt-what or hostnamectl.
# install first on Debian/Ubuntu: apt install virt-what
sudo virt-what

# or, on systemd systems:
hostnamectl | grep -i Virtualization
Both should agree with the first two checks. If systemd-detect-virt says kvm, /proc/user_beancounters is missing, and hostnamectl reports Virtualization: kvm, you have a genuine KVM VPS.
Run these before you commit to a longer billing term. A five-second check tells you whether the resources you are paying for are really dedicated, and it pairs well with hardening your box early, from firewall rules to DDoS protection.
Making the choice
If your workload touches the kernel, runs Docker or Windows, or simply needs performance you can count on, choose KVM and move on. Reserve OpenVZ for throwaway or ultra-budget Linux tasks where the shared-kernel limits genuinely do not matter to you.
Your next step is simple: pick a KVM plan sized to your workload, SSH in, and run systemd-detect-virt as your first command to confirm you got what you paid for. Browse ByteHosty's KVM VPS plans to find one that matches the CPU, RAM, and storage your project needs.
Questions covered
Is KVM better than OpenVZ?
For most workloads, yes. KVM gives each VPS a dedicated kernel and hardware-level isolation, so performance is more predictable and you can run custom kernels or Windows. OpenVZ is lighter but shares the host kernel and is more prone to resource contention.
Can I run a custom kernel on OpenVZ?
No. OpenVZ containers share the host kernel, so you cannot load custom kernel modules, run a different OS family, or use tools that require kernel-level access. KVM allows all of these because each VM boots its own kernel.
How do I check if my VPS is KVM or OpenVZ?
Run systemd-detect-virt on a systemd Linux system. It prints kvm for a KVM VM and openvz for an OpenVZ container. You can also check whether the file /proc/user_beancounters exists, since that file is only present in OpenVZ containers.
Does OpenVZ oversell RAM?
It can. OpenVZ historically supports burst and vSwap memory models that let providers allocate more RAM to containers than the host physically has, betting that not everyone uses their limit at once. KVM allocates memory to each VM directly.